Auto-Remediate Vulnerable Apps with Defender and Intune
October 21, 20267 min. read
Direct Answer
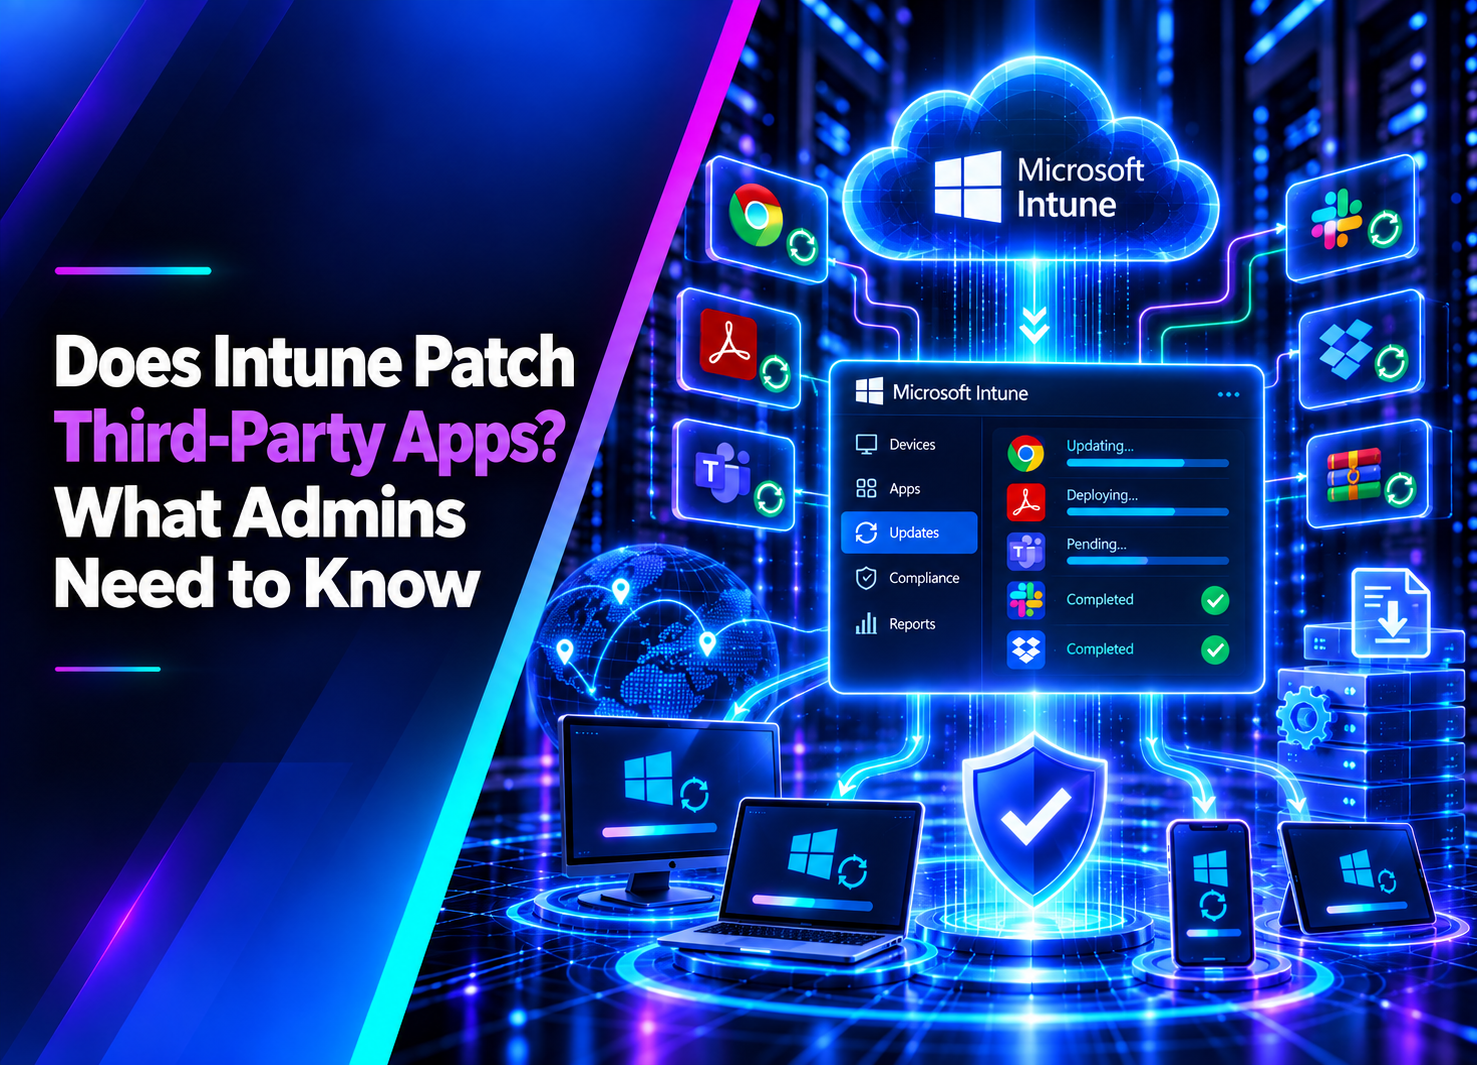
Microsoft Defender Vulnerability Management identifies vulnerable applications on your devices, but it does not package or deploy third-party updates. To close the loop, an updated package must exist in Intune and be assigned to the affected devices. Easy2Patch automates this: it evaluates the applications Defender reports as vulnerable, checks that the highest CVSS score meets your configured minimum and that a package exists in the catalog, then publishes the update to Intune and assigns it to the Entra ID groups you select.
Key Takeaways
Defender finds vulnerable software; Intune delivers the fix; Easy2Patch connects the two.
You control the minimum CVSS score, target groups, assignment purpose and exclusions.
Intune evaluates each device, so only devices with an older version install the update.
The feature is part of E2P Patch Manager’s Enterprise licence.
The gap between finding and fixing
Security teams often see a list of vulnerable applications in Microsoft Defender while endpoint teams manage deployments in Intune. Turning each finding into a tested package, a publication and an assignment is manual work, and every manual step adds delay. That delay is the window the “Don’t Make It Easy for Them” message asks organizations to close.
What Microsoft Defender Vulnerability Management provides?
Microsoft Defender Vulnerability Management builds a software inventory for onboarded devices, maps installed applications to known vulnerabilities (CVEs) and produces security recommendations. It tells you what is vulnerable and where. Delivering the updated application is still the job of a deployment system such as Intune.
How Easy2Patch closes the loop
Easy2Patch reads the applications that Defender Vulnerability Management reports as vulnerable.
It skips any application you have excluded on the Defender screen.
It checks that the application’s highest CVSS score is equal to or greater than your configured minimum score.
It confirms that a publishable package for the application exists in the Easy2Patch catalog
It publishes the update to Microsoft Intune.
It assigns the update to the Microsoft Entra ID groups you selected. If you select no group, vulnerabilities are evaluated across all managed devices.
Intune evaluates each device: devices with an older version install the update; devices without the application or already up to date are reported as Not Applicable.
Settings
What It Does
Enable / Disable
Turns the Defender integration on or off.
Auto Assignment
Lets Easy2Patch assign updates automatically to the selected groups.
Groups
Microsoft Entra ID groups that receive the updates and limit the scan scope.
Minimum Score
The CVSS threshold an application must meet to be published automatically.
Deployment Purpose
Available (users install from Company Portal) or Required (installs automatically).
Publishing Settings
Publish to Intune and, where used, to WSUS.
Publish Options
Overwrite the previously published application, or retire the old version and publish a new one.
Why a flagged application might not update
The application has no Defender mapping in the Easy2Patch catalog.
Its highest CVSS score is below the configured minimum.
It has been excluded on the Defender screen.
No publishable package exists in the catalog.
The device has not reported to Microsoft Defender for an extended period.
The update was published as Available, so users must install it from Company Portal.
A safe way to roll it out
Start with a pilot group and a high threshold, for example critical vulnerabilities only.
Use Required assignments for the pilot so you can measure real installation results.
Review Not Applicable and failed installations before widening the scope.
Lower the threshold or add groups in stages once results are stable.
Review exclusions monthly and give each one an owner and an expiry date.
Requirements
E2P Patch Manager with an Enterprise licence and a configured Intune connection.
Devices onboarded to Microsoft Defender for Endpoint with Defender Vulnerability Management data available
Microsoft Entra ID groups for targeting.
Frequently Asked Questions
Microsoft Defender Vulnerability Management identifies vulnerable software and recommends remediation, but it does not package or install third-party application updates itself. The update still has to be delivered by a deployment system such as Intune or Configuration Manager, either manually or through an integration that automates packaging and publishing.
Easy2Patch evaluates the applications that Microsoft Defender Vulnerability Management reports as vulnerable. An application is published automatically only if it is not excluded, its highest CVSS score is equal to or above the configured minimum score, and a publishable package for it exists in the Easy2Patch catalog.
Easy2Patch assigns the published update to the Microsoft Entra ID groups you select. If no group is selected, it evaluates vulnerabilities across all managed devices. Intune then checks each device: devices with an older version receive the update, while devices without the application or already up to date are reported as Not Applicable.
Common reasons are that the application has no Defender mapping or no publishable package in the catalog, its highest CVSS score is below the minimum, it has been excluded, or the device has not reported to Defender recently. If the update was published with an Available assignment, users must install it themselves from Company Portal.
There is no universal value. Many teams start with a high threshold, such as critical vulnerabilities with a CVSS score of 9.0 or above, on a pilot group, then lower it once deployments prove reliable. Combine the score with exploitation evidence, such as the CISA Known Exploited Vulnerabilities catalog, and with your own remediation targets.
Conclusion
Finding vulnerabilities is only half the job. Connecting Microsoft Defender Vulnerability Management to Intune through Easy2Patch turns findings into deployed fixes with thresholds, targeting and reporting you control.
Get started with our patch management software for freeAdvanced Patch ManagementGet 30 Days Premium Trial
Your cookie preferences
We use strictly necessary cookies to operate our website. In addition, and only with your consent, we would like to use functional and analytics cookies. For the categories you consent to, your data may be transferred abroad.
By accepting, you give your explicit consent to the processing of your personal data through cookies in the categories you have selected.
Cookie Preference Centre
You can enable or disable each category below. Strictly necessary cookies are required for the website to function and cannot be disabled. You may change your preferences at any time.
Strictly necessary cookies
Required for the operation of the website, session management, security, load balancing and recording your cookie preferences. These cookies do not require consent and cannot be disabled.
Always active
Functional cookies
Remember your language and display preferences and preserve form data. If disabled, your preferences will reset on each visit.
Analytics cookies
Allow us to measure visitor numbers and how the website is used, and to improve our content. Tool used: Google Analytics 4. Data may be transferred abroad.
I give my explicit consent to the processing of my personal data through cookies, and to its transfer abroad, in respect of the categories I have selected.
Your preferences have been updated. Cookies belonging to the categories you did not consent to have been deleted. Withdrawing your consent does not affect the lawfulness of processing carried out before the withdrawal.